Cybersecurity Emergencies: What to do and who to contact?

Cybersecurity Emergencies: Do You Know Who to Call?

Picture this: You’re working on a survey, and suddenly, your computer locks up. A ransom demand flashes across your screen, or perhaps you realise client data has been accessed without permission. Panic sets in—but do you know what to do next?

Cyber attacks and data breaches can happen to any business, and knowing who to call in an emergency can mean the difference between swift damage control and a full-blown crisis. In the UK, several key organisations handle cyber crime reports and offer guidance on what steps to take.

First Steps After a Cyber Emergency:

A cyber attack can be overwhelming, but immediate, measured action can significantly limit the damage.

If banking, payment systems or client funds may be involved, contact your bank immediately using a secure, unaffected device or phone line. Do not rely on email if your systems may be compromised.

Every situation is different, but the following steps provide a structured starting point.

1️⃣ Stay Calm and Isolate the Threat

If a device appears compromised, disconnect it from the internet and internal networks immediately. This helps prevent malware spreading or further unauthorised access.
Do not wipe or reset the device at this stage, as evidence may be needed and doing so may not fully eradicate the underlying issue.

2️⃣ Preserve Evidence

Avoid deleting suspicious emails, files or logs. If possible, take note of error messages, ransom notes or unusual activity.

This information will assist IT professionals or investigators.

3️⃣ Assess the Scope

Determine what may be affected:

  • A single device

  • Email accounts

  • Cloud systems

  • CRM or reporting platforms

  • Financial accounts

Understanding scope helps prioritise response.

4️⃣ Change Passwords – From a Clean Device

Using a secure, unaffected device, reset passwords for impacted accounts. Prioritise:

  • Email accounts

  • Banking

  • Cloud systems

  • Administrative logins

Enable multi factor authentication wherever possible.

5️⃣ Secure Your Systems

Engage professional IT support if available. Run reputable antivirus or endpoint security scans. Ensure operating systems and software are fully updated once systems are confirmed safe.

6️⃣ Review Financial and Client Risk

Check for unauthorised transactions, altered payment details or unusual communications. If financial information may be compromised, contact your bank immediately.

If personal data may have been exposed, consider whether notification obligations apply under UK GDPR.

7️⃣ Secure and Validate Backups

Confirm backups are intact and unaffected before restoring. Never restore from backups until you are confident they are clean.

8️⃣ Report the Incident

In the UK, cyber crime should typically be reported to:

  • Action Fraud (for fraud and cyber crime reporting)

  • The Information Commissioner’s Office if personal data is involved

  • Your insurer if you hold cyber cover

Early reporting can support investigation and insurance response.

These steps are just a starting point, and every situation is different. The right response will depend on the nature and severity of the cyber incident, and in some cases specialist advice may be required. The information shared here is intended as general guidance only and should not be taken as a guarantee of protection or a substitute for professional support.

That said, there are plenty of proactive steps you can take to reduce risk and strengthen your defences. There are also a wide range of resources available to help you prepare and act with confidence in the event of a breach. For further reading, take a look at some of our other security articles including:

🔹 RICS Guidance on Data Security
🔹 Cybersecurity for Surveyors: Protecting Your Business and Personal Data Online
🔹 Essential Cybersecurity Tools & Services

Who to Contact in a Cybersecurity Incident


Every incident is different. If finances are involved, contact your bank and alert the relevant people quickly. Reach out to IT support if available, and notify anyone who could be affected. Use common sense: verify who you’re speaking to and avoid sharing personal information.

Here’s a list of authorities and agencies to report to, depending on the type and severity—hopefully you’ll never need it.

Action Fraud – The First Stop for Cyber Crime Reports

What they do: Action Fraud is the UK’s national reporting centre for cyber crime and fraud. 

📌 Report online: Action Fraud Website
📌 Call: 0300 123 2040 to speak with a specialist advisor.

National Cyber Security Centre (NCSC) – For Serious Cyber Threats

What they do: The NCSC provides technical guidance and helps organisations manage cyber threats.

📌 Report online: NCSC Incident Reporting

Information Commissioner’s Office (ICO) – When Personal Data is Involved

What they do: If your breach involves personal data, you might be legally required to report it to the ICO within 72 hours to stay compliant with UK GDPR.

📌 Report online: ICO Breach Reporting Form

Local Police – When There’s an Immediate Threat or Loss

What they do: If a cyber incident results in financial loss or involves criminal behaviour, contacting the police may be necessary.

📌 England & Wales: Contact your local police force.
📌 Scotland: Report to Police Scotland.
📌 Northern Ireland: Contact the Police Service of Northern Ireland (PSNI).

National Crime Agency (NCA) – For Major Cyber Attacks

What they do: The NCA investigates large-scale cyber crime and coordinates responses with other agencies.

📌 Referral process: Reports typically go through Action Fraud or local police, who escalate cases to the NCA when necessary.
Cyber threats are constantly evolving, and the best way to protect your business is by staying one step ahead. Prevention is just as important as having a recovery plan. Taking proactive measures can significantly reduce your risk of falling victim to an attack.

To minimise risk, make sure you:
✔️ Back up your data regularly – Ensure your backups are secure, up to date, and stored separately from your main network to prevent ransomware from locking you out.
✔️ Use multi-factor authentication (MFA) for extra security – Adding an extra layer of protection makes it much harder for cybercriminals to access your accounts, even if they steal your password.
✔️ Train your team to recognise phishing scams – Educating employees on how to spot suspicious emails, fake login pages, and social engineering tactics can prevent breaches before they happen.
✔️ Keep software and security systems up to date – Regular updates help close vulnerabilities that hackers might exploit.
✔️ Have a response plan so everyone knows what to do if an attack happens – A well-prepared team can act quickly to contain threats, limit damage, and keep your business running smoothly.

Cyber incidents can be overwhelming, but with the right contacts and a solid plan, you can take control of the situation.

🛡️ How Survey Booker Helps Protect Your Business 🛡️

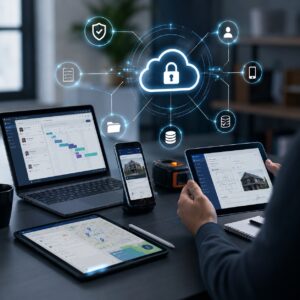
While knowing who to call in a cyber emergency is crucial, prevention is always better than cure. Survey Booker provides a secure, cloud-based CRM designed to protect your data, streamline operations, and reduce cybersecurity risks.


✅ Encrypted Data Storage – Keep sensitive client and project information safe.
✅ Secure Client Communication – Reduce phishing risks with built-in messaging.
✅ Access Controls & Permissions – Ensure only the right people see the right data.
✅ Automated Workflows – Minimise human error and security vulnerabilities.
✅ Regular System Updates – Stay protected against evolving cyber threats.

✅ ISO 27001 Information Security Certified – We’re externally audited to check our security processes.


With Survey Booker, you’re not just managing your surveys efficiently—you’re adding an extra shield against cyber risks. Stay protected, stay compliant, and keep your business running smoothly.


🔐 Want to learn more? Click here to request a demo or call back from a member of the team.

Scroll to Top