Survey Booker Editorial · Security
The Security Blind Spot in Modern Surveying
What we discussed at the Surveying Updates Roadshow in Bristol and why every surveying firm should be reviewing its technology suppliers.
When surveyors talk about compliance, the conversation usually centres on professional standards, terms of engagement, inspection processes, report quality and maintaining an adequate audit trail.
Information security does not always receive the same attention.
Yet modern surveying businesses are no longer operating through clipboards, paper diaries and filing cabinets. The inspection may still take place at the property, but almost every process surrounding it is now digital.
Client enquiries arrive through online platforms. Personal details are entered into CRM systems. Appointments are managed in cloud-based diaries. Terms of engagement are issued electronically. Payments are processed online. Site notes and photographs are stored digitally. Reports move between software platforms, email systems and client portals.
Each system may make the surveyor’s life easier. It may also hold, access or transmit information upon which the business and its clients depend.
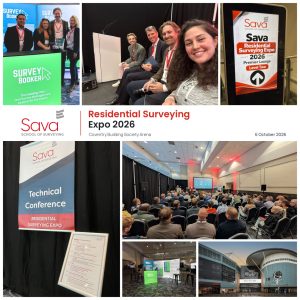
That was the subject we were invited to explore at the recent CPD Surveying Updates Roadshow, held at the University of the West of England in Bristol.
Our session was titled: Security: the ignored and forgotten essential in modern surveying businesses.
What surprised us most was not a lack of concern among the surveyors attending. It was how many had understandably assumed that the technology they were already using had been subjected to more extensive security assessment than may actually be the case.
That creates an important question for every surveying practice:
The survey is only one part of the data journey! Surveyors are trained to identify risk within a property, follow professional standards and produce reports capable of withstanding scrutiny.
The same level of scrutiny should be applied to the systems surrounding that work.
Consider how much information may pass through a surveying firm during an ordinary instruction:
- Names, addresses and contact details
- Property access arrangements
- Client correspondence
- Financial and payment information
- Inspection notes and photographs
- Valuation or survey data
- Reports and supporting evidence
- Complaints and claim-related correspondence
- Employee and subcontractor information
This information may be distributed across lead-generation services, CRM platforms, report-writing software, cloud storage, email providers, accounting systems, payment processors and increasingly AI-enabled tools.
The security of the surveying business therefore depends not only on its own computers and passwords, but also on the suppliers forming its wider technology chain.
That does not mean technology should be feared or avoided. Quite the opposite. Good technology can improve consistency, reduce human error and create far stronger operational records.
It does mean that selecting a system because it is well known, industry specific or included within a professional technology programme should not replace the firm’s own due diligence.
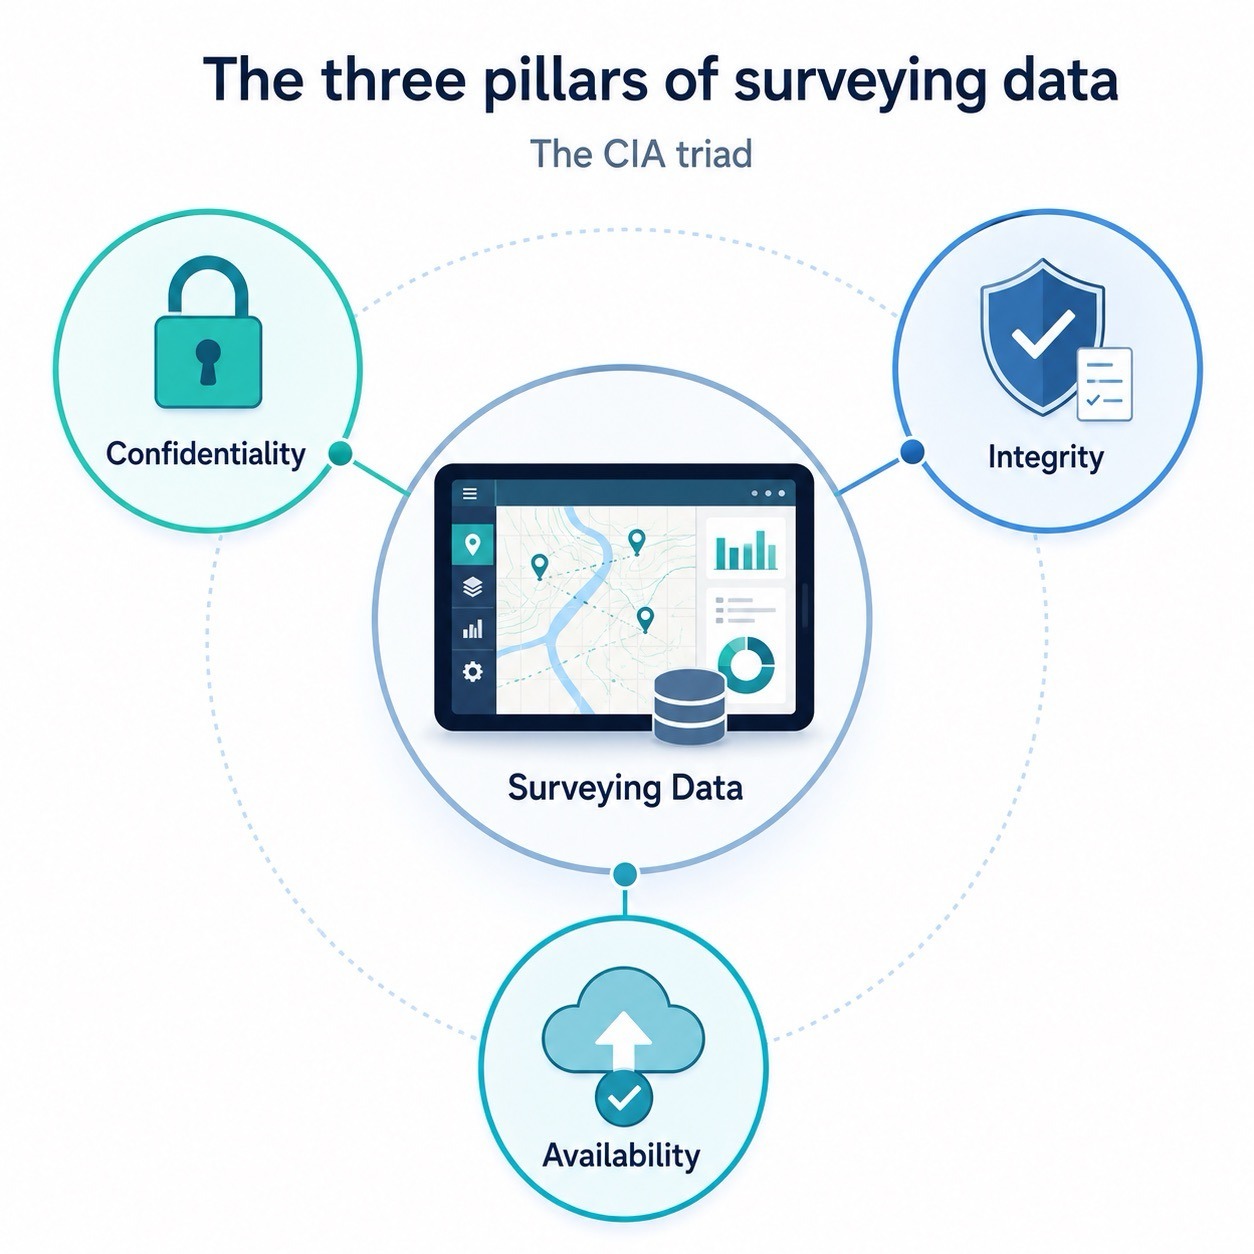
The three pillars of surveying data
The three pillars of surveying data
Information security is often presented as an impenetrable world of technical terminology. In reality, it can be understood through three straightforward principles: confidentiality, integrity and availability.
Together, these are often known as the CIA triad.
Confidentiality
Confidentiality concerns who can see information and whether access is limited to the right people.
For a surveying firm, this might include protecting client details, property access information, tender documents, development plans, financial information, photographs and confidential correspondence.
Questions of confidentiality extend beyond whether a system has a password. Firms should understand how access is controlled, whether multifactor authentication is available, how permissions are allocated and what happens when an employee or subcontractor leaves.
Integrity
Integrity means being able to trust that information remains accurate, complete and unaltered.
This is particularly important in a profession where records may later be relied upon to explain what was inspected, what was reported and how a professional conclusion was reached.
A missing photograph, overwritten inspection note, corrupted report or altered document version can create significant professional and legal difficulties. Firms should therefore consider whether their systems maintain reliable audit trails, document histories and controlled access to important records.
Availability
Availability means being able to access information when it is required.
A secure system that is regularly unavailable, poorly backed up or incapable of recovering from an incident still presents a serious operational risk.
Surveyors working remotely need dependable access to appointments, client details, property information and job records. The business also needs to know that, should a supplier experience an outage or cyber incident, appropriate backup, recovery and continuity arrangements are in place.
Understanding assurance
No certification, Cyber Essentials and ISO 27001
One of the areas we explored during the session was the difference between having no recognised security certification, holding Cyber Essentials and being certified to ISO 27001.
These should not simply be treated as three badges of increasing prestige. They provide different types and levels of assurance.
No recognised certification
The absence of certification does not automatically mean that a supplier is unsafe.
A business may have sensible security controls without choosing to pursue formal certification. However, the customer may then need to conduct more detailed due diligence to understand what those controls are and how their effectiveness is assessed.
Statements such as “we take security seriously” or “your data is securely hosted” should be the beginning of the conversation, not the conclusion.
Cyber Essentials
Cyber Essentials is a UK Government-backed standard designed to help organisations protect themselves against common cyberattacks.
It provides an important practical baseline, addressing areas such as secure configuration, user access, malware protection, firewalls and security updates.
For many businesses, it is a valuable starting point and evidence that fundamental technical protections have been considered.
However, it should not be confused with a complete information-security management system. Its primary focus is protection against common forms of attack rather than the full range of organisational, supplier, people and process risks that can affect information.
ISO 27001
ISO 27001 takes a broader, risk-based approach.
It requires an organisation to establish, maintain and continually improve an information security management system. This reaches beyond individual technical controls and considers how security is governed throughout the business.
Depending upon the organisation and the scope of its certification, this may include:
- Risk assessment and treatment
- Policies and responsibilities
- Employee awareness and training
- Access and identity management
- Supplier and subcontractor risk
- Incident management
- Business continuity
- Data retention and disposal
- Internal auditing
- Management review
- Continual improvement
Certification does not mean that a business can never suffer an outage, mistake or cyber incident. No credible provider should make that promise.
What it does demonstrate is that the organisation has implemented a structured information-security management system within a defined scope and that this has been independently assessed.
When reviewing a supplier, firms should not simply ask whether it displays an ISO logo. They should request confirmation of the exact standard, the scope of certification, the certification body and whether the certificate remains current.
Partnership is not certification
Does an industry partnership amount to a security endorsement?
The RICS Tech Partner Programme plays a valuable role in bringing together technology businesses operating across the land, property and built-environment sectors. It encourages collaboration, market insight and the adoption of technology within the profession.
However, inclusion within such a programme should not be treated as a replacement for a surveying firm’s own supplier checks.
The published programme terms require prospective partners to complete an application and pass RICS due-diligence investigations. Importantly, those same terms also state that Tech Partner branding must not be represented as formal endorsement of any partner’s solution by RICS.
A technology business may participate in a respected professional programme without its individual software platform being certified to a particular information-security standard.
This is not criticism of the programme, nor a suggestion that RICS should assume responsibility for every system used by the profession. It is simply a reminder that participation, collaboration and security certification are not interchangeable.
The ultimate responsibility for selecting suitable suppliers remains with the surveying firm.
Where a supplier processes personal data on the firm’s behalf, the business must satisfy itself that the provider can offer appropriate protection. That responsibility does not disappear because the provider is well known, widely used or associated with an industry body.
Supplier due diligence
What should you ask your technology suppliers?
Supplier due diligence does not have to become an enormous procurement exercise. The depth of assessment should be proportionate to the sensitivity of the information involved and the level of access being granted.
However, every surveying firm should be able to answer some fundamental questions:
A trustworthy supplier should be willing to answer reasonable questions. Evasive, generic or heavily sales-led responses should prompt further investigation.
Operational resilience
Security and efficiency should support one another
Security is sometimes portrayed as the enemy of convenience. In a well-designed operation, the opposite should be true.
Disconnected systems, uncontrolled spreadsheets, shared logins and information scattered across individual inboxes can create both inefficiency and risk.
A secure operational platform should help a surveying firm create:
- Consistent processes
- Clearly allocated responsibilities
- Appropriate user permissions
- Reliable audit trails
- Centralised job records
- Controlled document histories
- Repeatable compliance workflows
- Effective employee onboarding and removal
- Better oversight of integrations and data movement
Automation does not create compliance by itself. It can, however, make good practice easier to repeat and easier to evidence.
This is where a CRM and survey management system should become more than a booking diary.
Our approach
Why Survey Booker pursued ISO 27001 certification
Survey Booker holds information that supports the day-to-day operation of surveying businesses.
That responsibility is precisely why we chose to undertake the process of becoming ISO 27001 certified.
We did not view it as a marketing badge or a one-off compliance exercise. We wanted information security to be embedded into the way our own business assesses risk, manages access, works with suppliers, responds to incidents and continually improves.
Certification does not remove the responsibility to remain vigilant. In many respects, it formalises that responsibility.
It also gives our customers independent assurance that our information-security management system has been assessed against an internationally recognised standard.
A practical starting point
Begin with a simple technology review
Reviewing technology risk does not necessarily mean replacing every system currently in use.
A sensible first step is to map the technology within the business:
- Which systems are being used?
- What information enters each one?
- Who has access?
- Which systems connect to one another?
- What evidence of security has each supplier provided?
- Could the business retrieve its records and continue operating if one became unavailable?
The most striking lesson from our Bristol session was not that surveyors are careless with information.
It was that the industry has adopted technology rapidly, while many of the questions surrounding supplier assessment have remained in the background.
That now needs to change.
Surveyors apply professional judgement every day. They inspect, question, document and avoid relying upon unsupported assumptions.
The same principles should be applied to technology.
The security blind spot